
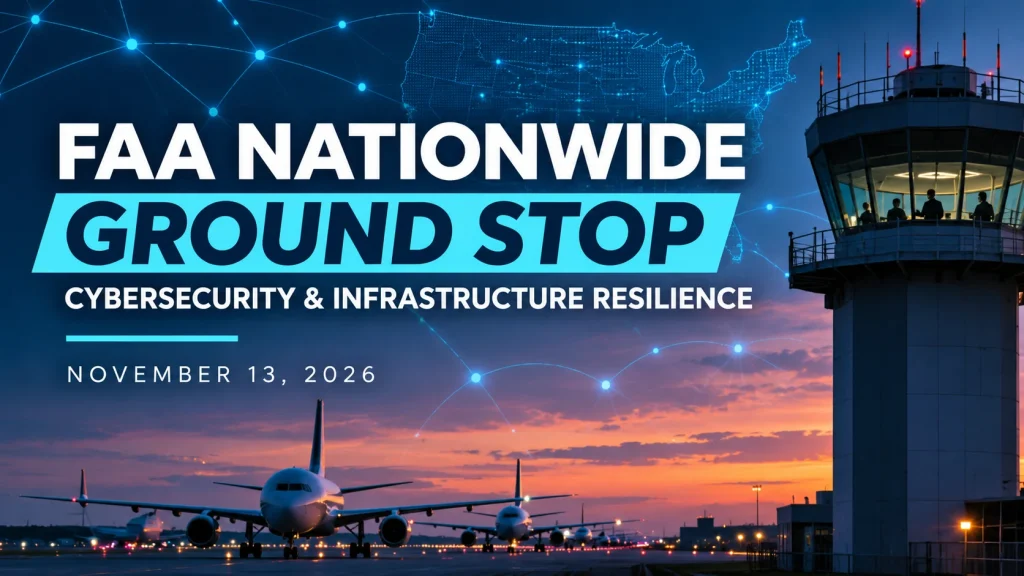
Published November 13, 2026. Updated November 14, 2026 with officials’ network-equipment explanation and restoration details. Developing investigation. The Federal Aviation Administration (FAA) ordered a nationwide ground stop on November 13, 2026, after a telecommunications disruption affected air traffic control communications across the United States. The interruption affected the nation’s 22 regional air traffic control centers and disrupted departures across the country.
Homeland Security Secretary Markwayne Mullin said there was no indication of a cyberattack at the time of his remarks. Investigators had not yet published a definitive root-cause analysis. That distinction matters: an outage is not evidence of hacking, but an initial statement that no cyberattack has been identified is not the same as a completed technical investigation.
For Blueclone Networks, the bigger question is about resilience. Why can failures in critical communications infrastructure create nationwide disruption, and what must government agencies and private businesses do to prevent, detect, and recover from such failures?
November 14 Update: FAA Outage Linked to Network Equipment During Telecommunications Upgrade
November 14, 2026: Transportation Secretary Sean Duffy described a network equipment issue during telecommunications modernization work involving contractor L3Harris Technologies. According to Duffy’s account, work to replace legacy copper connections with fiber was associated with a router that began flooding other parts of the FAA network, disrupting communications and data services.
What investigators are still determining: Whether faulty equipment, an installation or configuration mistake, or another technical factor initiated the problem. The full sequence of events, network dependencies and effectiveness of safeguards have not yet been documented in a final public root-cause report. Earlier reporting suggested a Chicago-area origin; that preliminary geographic detail should not be treated as a confirmed finding.
Operational status: The FAA lifted the nationwide ground stop on Friday evening, November 13. Officials reported restored air traffic control operations on Saturday, although airlines continued working through residual delays and cancellations.
Why it matters: A network change that affects interconnected services raises critical questions about maintenance windows, change validation, routing controls, fault isolation, independent failover paths and recovery testing. The incident is not evidence of a cyberattack; officials have reported no indication of malicious cyber activity.
Sources: NPR reporting, November 14; U.S. Department of Transportation statement. Technical investigation remains ongoing.
What Happened During the November 13 FAA Nationwide Ground Stop?
According to reporting by the Associated Press, the FAA halted departures nationwide as a safety precaution following communications failures involving regional air traffic control centers. Aircraft already airborne were permitted to continue toward safe landings, while the disruption created delays and cancellations for travelers and airlines.
Officials initially described the problem as a telecommunications outage. Subsequent statements on November 14 linked the disruption to network equipment during a contractor-led telecommunications upgrade, although a final technical root-cause report remains outstanding. The nationwide restriction was lifted Friday evening, with some airline disruption continuing afterward. See Associated Press coverage for the contemporaneous reporting.
Was the FAA Ground Stop Caused by a Cyberattack?
There is no publicly established evidence, as of the November 14 update, that a cyberattack caused the November 13 ground stop. Secretary Mullin said there was no indication of one. That statement should be reported accurately rather than dismissed or portrayed as proof of a cover-up.
Officials have since described a router-related network problem during telecommunications modernization. That narrows the reported technical scenario, but it does not by itself establish whether the initiating cause was defective equipment, a configuration or installation error, or another operational factor. A documented investigation is needed to distinguish among these possibilities.
The responsible questions are therefore technical: What triggered the reported router flooding? Why did the effect propagate through interconnected services? Which fault-isolation and failover mechanisms operated as designed? How were malicious causes evaluated? And what changes will prevent recurrence?
The GAO Warned About Aviation Cybersecurity Risks Before the Outage
On September 21, 2026, the U.S. Government Accountability Office (GAO) published GAO-26-108439, Aviation Cybersecurity: Enhanced Air Safety Requires FAA to Better Mitigate Threats to Aircraft Communications. The report identified shortcomings in the FAA’s approach to risks involving radio-frequency interference, spoofing, jamming, communications security, monitoring, and coordination.
Incomplete Risk and Mitigation Assessments
GAO found that the FAA had not completed certain risk and mitigation assessments or updated security documentation needed to address identified spectrum-related threats. Without a complete view of risks, prioritizing mitigation becomes more difficult.
Gaps in Real-Time Threat Monitoring
GAO reported that the FAA lacked a defined, comprehensive real-time monitoring and detection capability for all spectrum-related threats. That finding concerns the threats and systems examined in the GAO audit; it does not prove that the November 13 telecommunications outage went undetected because of those gaps.
Authentication and Data Protection Weaknesses
The report also described limitations involving authentication, encryption, and protocol design in aviation text-based communications applications, including ACARS and CPDLC. GAO warned that such weaknesses could expose communications to interception or spoofing and recommended stronger protections.
Cybersecurity Coordination and Accountability
GAO found opportunities to improve coordination and information sharing among government and aviation-industry stakeholders. It issued nine recommendations, with the Department of Transportation concurring on behalf of the FAA.
Important context: The GAO audit assessed specific aviation communications and spectrum-related cybersecurity risks. It did not investigate the November 13 event and does not demonstrate that the vulnerabilities it identified caused the nationwide ground stop.
Even If This Was Not a Cyberattack, the Infrastructure Questions Remain
A purely accidental failure can be as operationally disruptive as a malicious incident. The central resilience challenge is to design critical systems so that the failure of one component, network, service provider, or control plane does not create disproportionate downstream consequences.
Modernization and accountability: Secretary Duffy has called for substantial additional investment in air traffic control modernization. Funding can help replace aging systems, but resilient outcomes depend on architecture, safe change procedures, independent testing, monitoring, and documented recovery performance. A fiber upgrade alone cannot guarantee that failures will remain contained.
In September 2026, GAO also examined the FAA’s ambitious air traffic control modernization effort and emphasized the need for better cost and schedule planning. Modernization is not simply replacing aging hardware. It must include secure architecture, tested failover, observability, supplier risk management, and recovery exercises. See GAO-26-107992 on air traffic control modernization.
Five Questions the Public Deserves Answered
- Root cause: What caused the reported router flooding during telecommunications upgrade work?
- Scope: How did the network disturbance spread beyond the equipment being changed, and what isolation controls were in place?
- Cybersecurity: What evidence was used to assess and exclude malicious activity, and what remains under investigation?
- Resilience: Which redundancy, change-control, failover, and incident-response mechanisms worked or failed?
- Accountability: What remediation deadlines, independent reviews, and public progress reports will follow?
Not every technical detail can be disclosed publicly without creating new security risks. But officials can provide meaningful timelines, independently validated findings, and remediation commitments without exposing sensitive configurations.
What Businesses Can Learn from the FAA Disruption
Most organizations do not operate air traffic control systems, but they share the same fundamental exposure: critical operations depend on networks, cloud platforms, communications services, vendors, and systems that can fail unexpectedly.
1. Map Critical Dependencies
Identify the applications, identity services, internet circuits, telecommunications providers, and vendors that support revenue-generating and safety-critical processes. Document shared dependencies that could defeat supposedly independent backups.
2. Test Redundancy Instead of Assuming It Works
Validate alternate connectivity, communications channels, recovery paths, and failover procedures. A second connection offers limited protection if it shares the same upstream failure point.
3. Strengthen Security and Operational Monitoring
Correlate endpoint, network, identity, application, and provider alerts. Monitor for both suspicious behavior and ordinary service degradation, and ensure teams know when and how to escalate anomalies.
4. Rehearse Incident Response and Business Continuity
Run tabletop exercises that include uncertain root causes, unavailable vendors, disrupted communications, and prolonged service interruptions. Assign decision-makers and establish recovery priorities before an incident occurs.
5. Demand Evidence from Critical Vendors
Ask providers how they test resilience, handle security incidents, communicate outages, and validate recovery. Contractual service levels alone are not a substitute for technical assurance.
How Blueclone Networks Helps Organizations Build Resilience
Blueclone Networks provides security-first managed IT, co-managed IT, cybersecurity, cloud services, and business continuity support to organizations in New Jersey, Eastern Pennsylvania, and beyond. Our work focuses on reducing operational risk through practical controls, proactive monitoring, resilient technology architecture, and tested response procedures.
For healthcare, financial services, legal, life sciences, and other regulated organizations, a resilience review can identify critical dependencies, evaluate recovery readiness, and align security controls with operational and compliance requirements.
To discuss your organization’s cybersecurity and infrastructure resilience, contact Blueclone Networks.
Sources and Ongoing Updates
- NPR: Network equipment issue during FAA telecommunications upgrade (November 14, 2026)
- U.S. Department of Transportation: Ground-stop lifting and official updates
- CNN: Preliminary reporting about network routers and the FAA communications disruption (November 13, 2026)
- Associated Press: November 13, 2026 nationwide ground stop and official statements
- U.S. GAO: Aviation Cybersecurity, September 21, 2026 (GAO-26-108439)
- U.S. GAO: FAA and TSA Cybersecurity Coordination, July 16, 2026
- U.S. GAO: Air Traffic Control Modernization, September 2026
- Federal Aviation Administration
- NIST Cybersecurity Framework 2.0
Incident update — November 14, 2026: This article now incorporates officials’ account of a network-equipment issue during telecommunications modernization and the restoration of FAA operations. The precise initiating fault and full propagation path remain under investigation. Earlier Chicago-area router reporting was preliminary. The GAO findings discussed here concern separate cybersecurity and modernization reviews; they do not establish the cause of this incident. Blueclone Networks will update this article as verified technical findings and corrective actions become available.
Frequently Asked Questions
The FAA stopped departures nationwide after a telecommunications disruption affected air traffic control communications. The precaution was intended to protect flight safety while technicians investigated.
As of November 14, officials have reported no indication of malicious cyber activity. They have described a router-related issue during telecommunications upgrade work, but a final technical root-cause report was not yet available.
A September 2026 GAO audit identified gaps in risk assessments, spectrum-threat monitoring, communications protections, and stakeholder coordination. Those findings do not establish the cause of the November 13 outage.
Yes. Officials have described a router-related network problem during FAA telecommunications upgrade work. Shared dependencies and insufficient fault isolation can allow disruptions to spread, although the exact failure path in this incident still requires investigation.
Map critical dependencies, test failover, improve security and service monitoring, rehearse incident response, evaluate vendors, and maintain alternative communications and recovery procedures.


